Risk Management & Security Hardening Services
Vulnerabilities can only be exploited if your systems leave doors open. Exelon Circuits locks down your digital attack surface through disciplined operating system hardening, firewall rule tightening, and immutable backup architectures.
We apply CIS Benchmarks and zero-trust principles to eliminate default credentials, close unused network daemons, enforce least-privilege policies, and safeguard your infrastructure against ransomware.
System hardening & defense capabilities
Comprehensive technical solutions engineered for security, reliability and measurable business outcomes.
Server & Operating System Hardening
Applying CIS Level 1 and Level 2 configuration baselines across Linux and Windows server environments.
Ransomware Defense Architecture
Deploying immutable storage buckets, off-site air-gapped snapshots, and automated anomaly alerts.
Database Security Lockdown
Hardening SQL Server, PostgreSQL, and MySQL against injection, unauthorized dumps, and weak grants.
Privileged Access Management (PAM)
Restricting administrator credentials, enforcing multi-factor authentication, and logging session recordings.
Threat Modeling & Surface Reduction
Systematically mapping data flows and deprecating legacy protocols (SMBv1, Telnet, TLS 1.0/1.1).
Network Switch & Firewall Hardening
Securing router control planes, disabling unencrypted management protocols, and isolating management VLANs.
Zero Trust Micro-Segmentation
Confining lateral attacker movement so a single compromised machine cannot access core databases.
Automated Compliance Auditing
Scheduling continuous configuration drift scripts that flag unintended security setting changes.
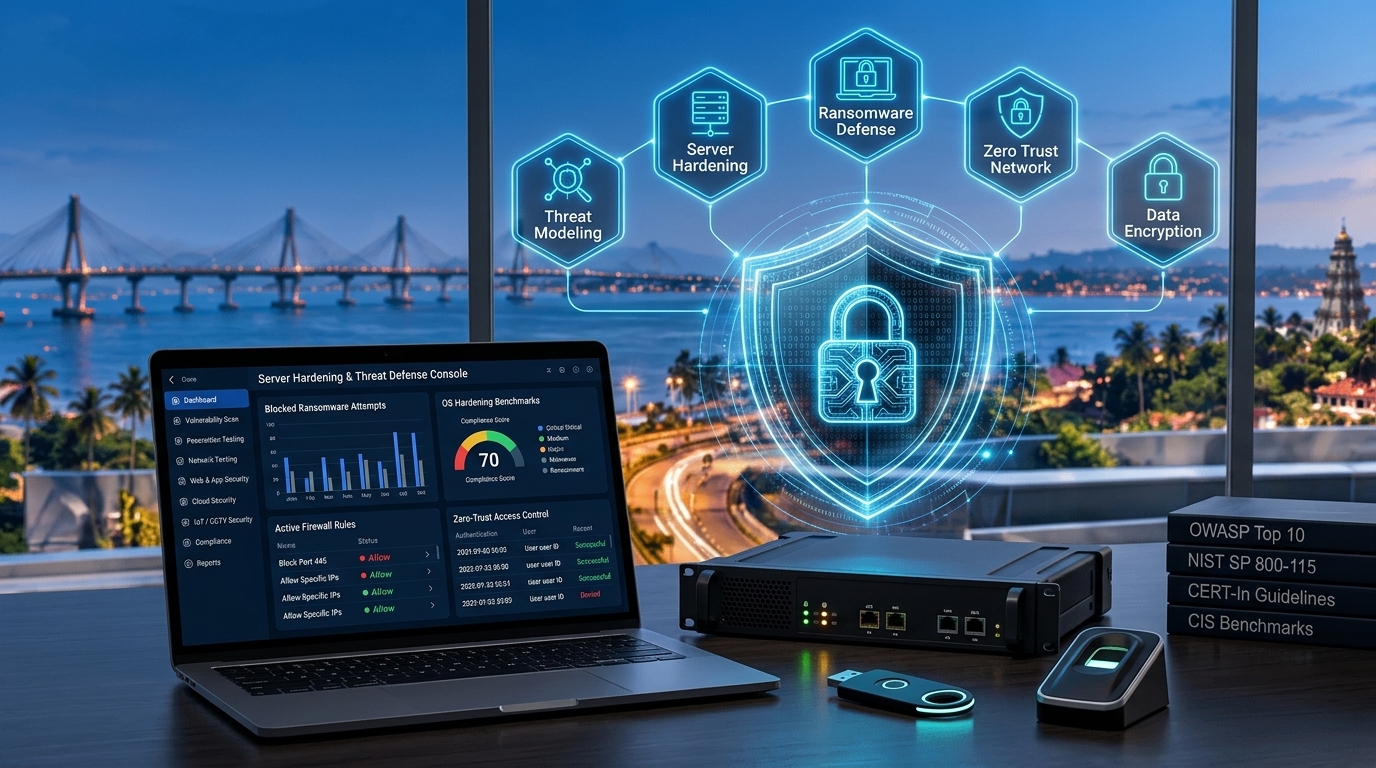
Who requires system hardening
Organizations maintaining mission-critical databases and financial records:
Financial Institutions & Fintechs
Protecting core accounting ledgers and payment processing nodes from malware infiltration
Manufacturing ERP Operators
Preventing ransomware from locking factory assembly lines and dispatch servers
Hospitals & Diagnostic Centers
Ensuring 24/7 availability of critical patient monitoring systems and medical imaging archives
SaaS Platforms & Cloud Startups
Hardening production Kubernetes clusters and multi-tenant cloud storage against lateral movement
Our 5-step hardening lifecycle
A disciplined, transparent delivery sequence ensuring predictable timelines and verified deliverables.
Attack Surface Mapping
Scanning and cataloging exposed services, default ports, and outdated cryptographic algorithms.
Hardening Baseline Definition
Customizing CIS benchmark policies to match your specific application dependencies.
Staging Validation
Applying hardening configurations in a sandbox or test environment to verify operational compatibility.
Scheduled Production Rollout
Deploying scripted hardening policies during approved maintenance windows with zero business disruption.
Post-Hardening Verification
Running verification vulnerability scans to confirm the attack surface has been closed.
Security standards enforced
CIS Benchmarks Level 1 & 2
Internationally recognized consensus guidelines for operating systems and servers
NIST SP 800-123
Guide to General Server Security recommendations and baseline protocols
MITRE ATT&CK Matrix
Defensive mappings directly blocking common attacker tactics and privilege techniques
Proven Deployments & Results
Real client solutions engineered, tested, and running in production.
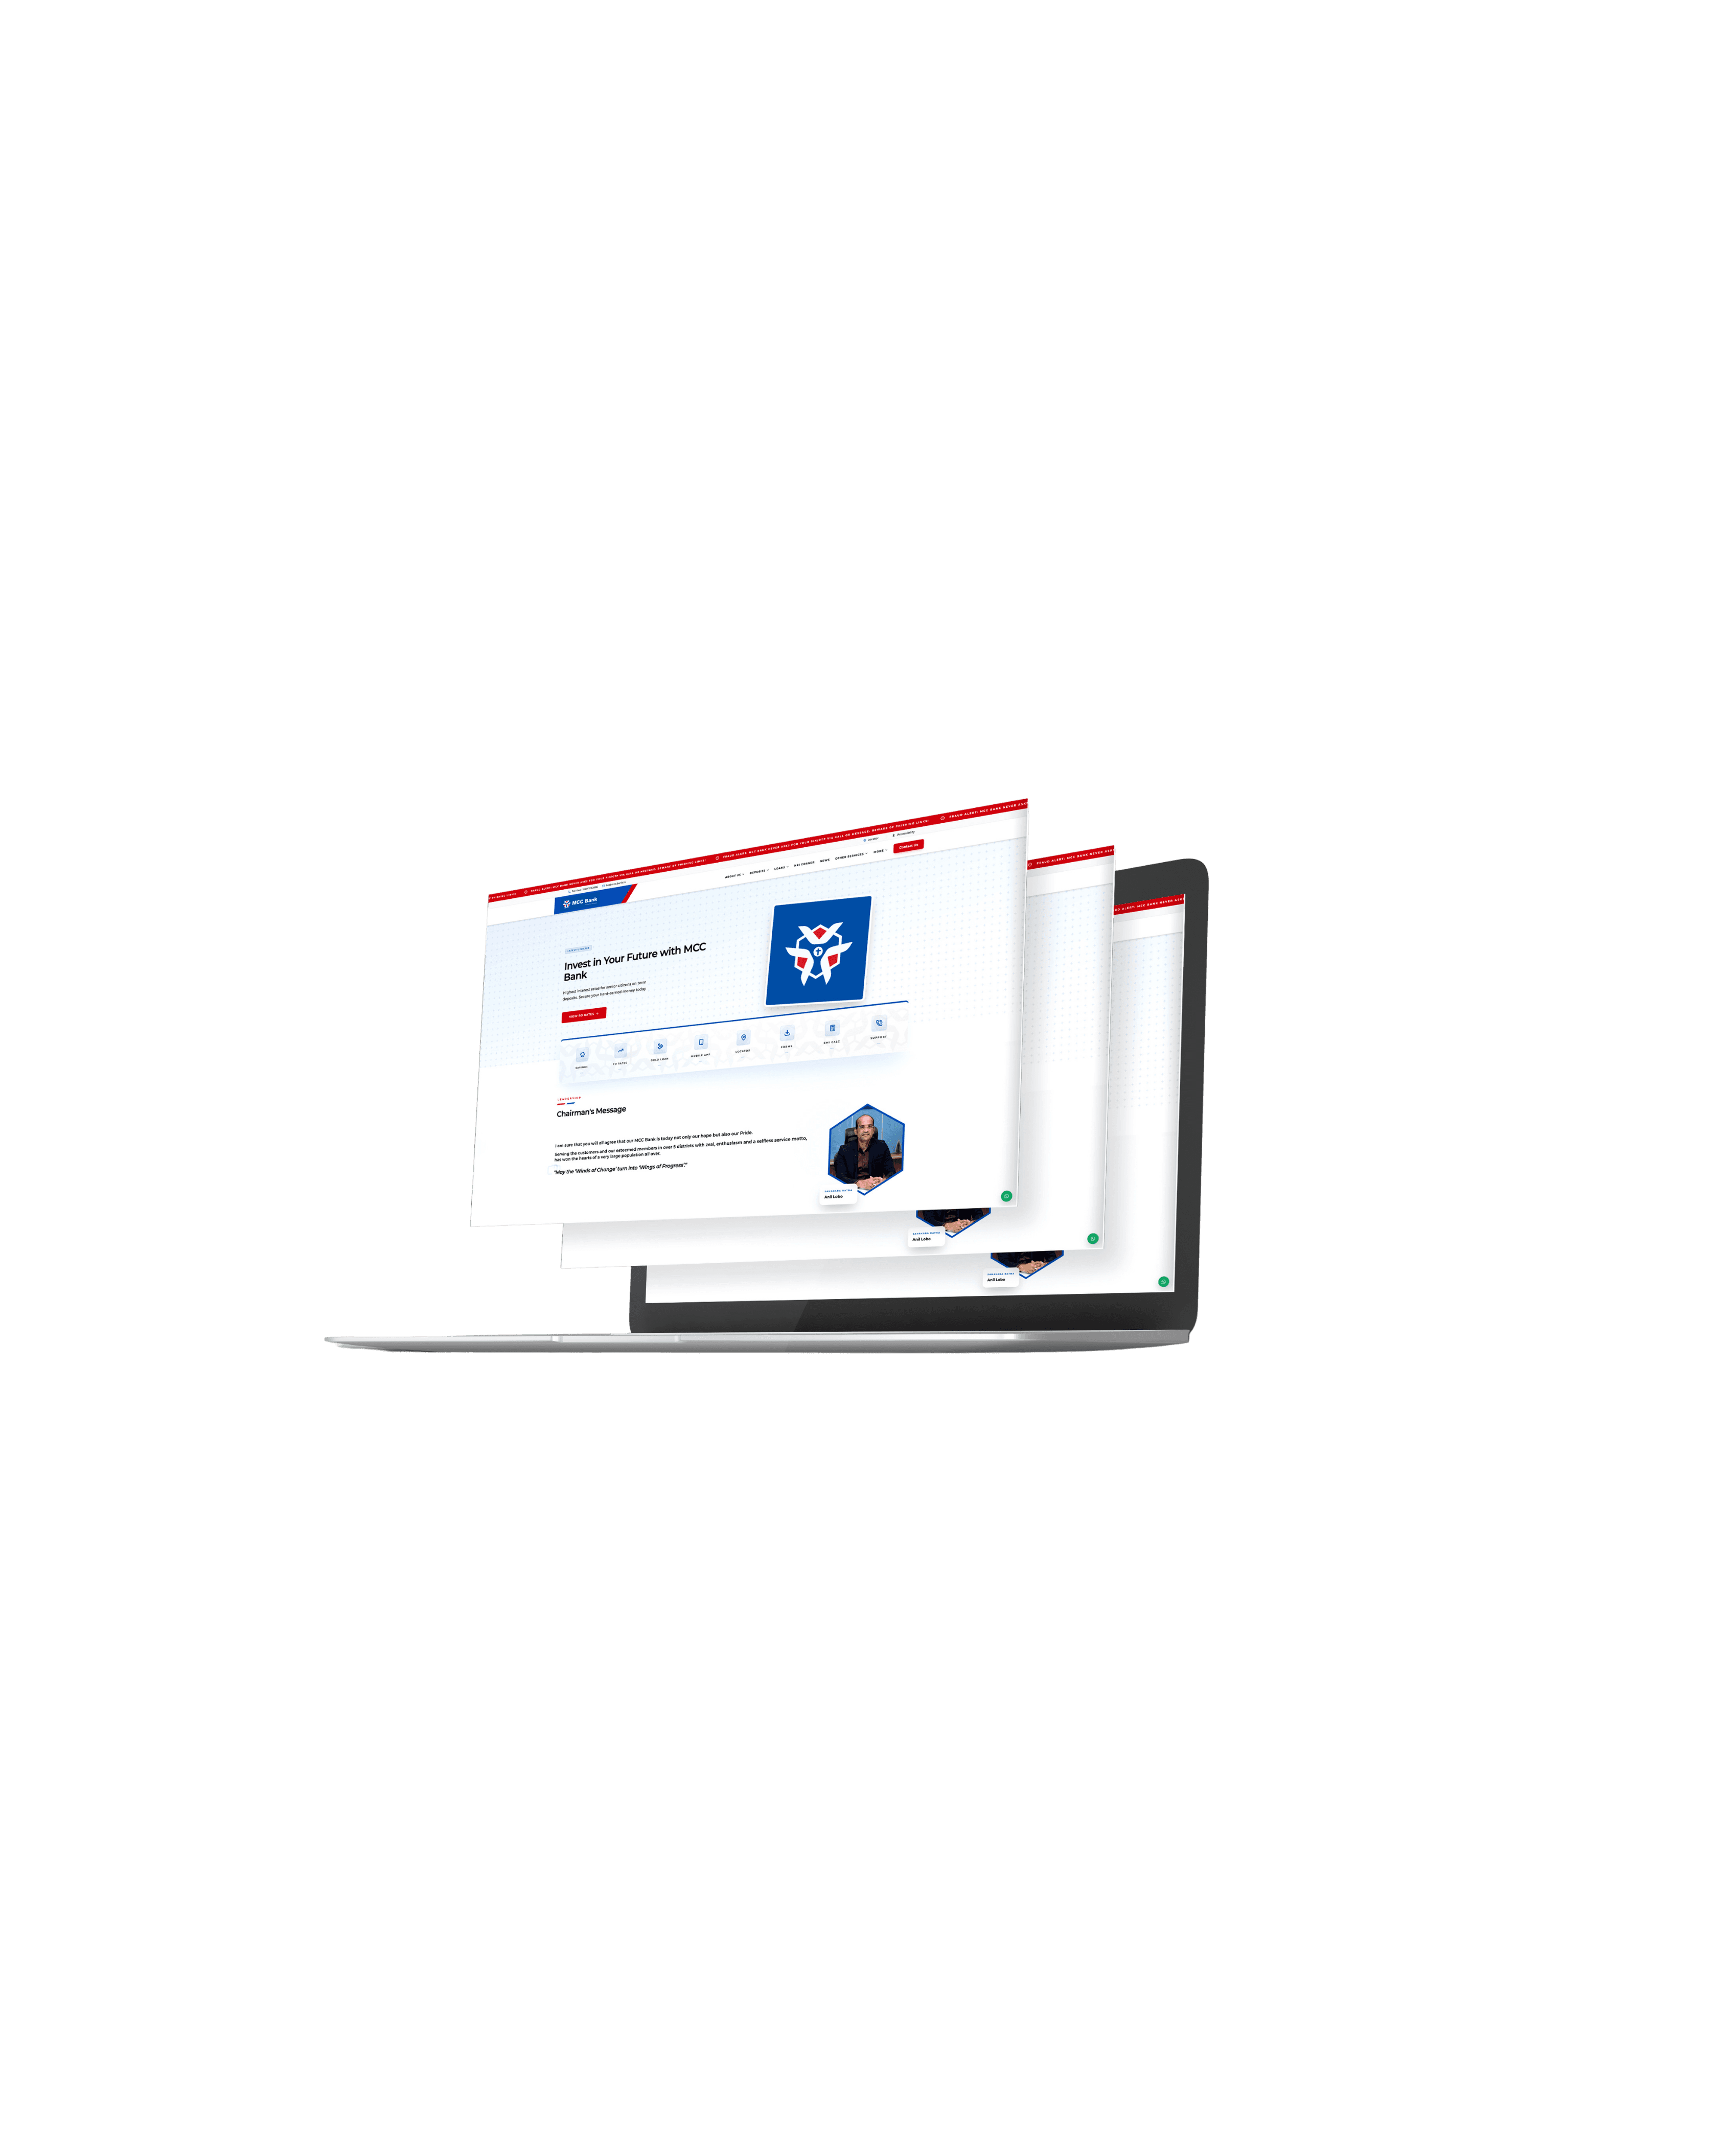
MCC Bank
A modern, mobile-responsive banking website redesign improving usability, navigation, and customer trust. The upgrade delivered better mobile experience and improved search engine visibility for the institution.
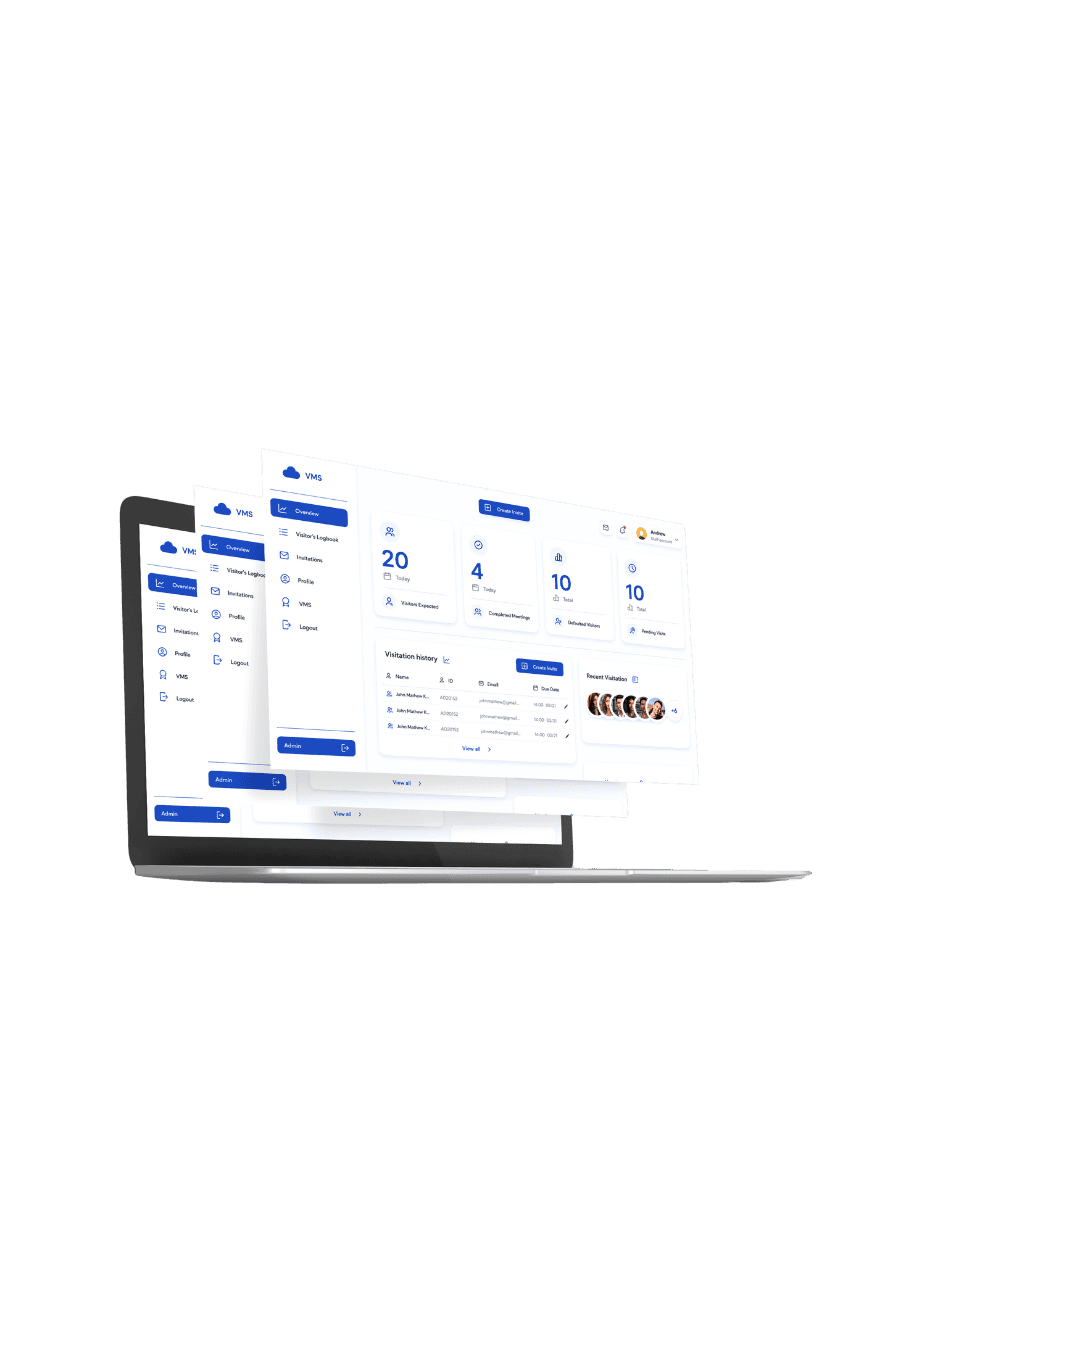
Visitor Management System
A digital check-in platform replacing manual paper logs with secure, contactless visitor registration and badge printing. It improved workplace security and provided real-time insights into visitor traffic.
What Risk Management & Hardening Costs
Hardening contracts are priced transparently per system node:
Why Partner with Exelon Circuits?
Local presence, certified engineering personnel, and dedicated post-deployment support.
Hands-on systems engineers who configure Linux and Windows kernels daily, not theoretical paper auditors
Strict rollback scripts tested before every deployment to eliminate any risk of service interruption
Direct on-site engineering dispatch from Surathkal for enterprise clients in Mangalore and Udupi
Complete handover documentation outlining exact configurations applied for future IT maintenance
Frequently Asked Questions
Clear answers regarding deployment timelines, technical scope, and ongoing support.
Lock down your servers before ransomware strikes
Request a rapid attack-surface review from our senior infrastructure hardening team.